Eagle provides a free newsletter each month for customers on HIPAA and Meaningful Use security matters. You can subscribe to the Eagle Healthcare IT Security Newsletter free.
Recently, entire hospital networks have been shut down for time periods between 3 days and 3 weeks due to ransomware attacks. What can be done? Fortunately, there are established best practices which can prevent one of these attacks in the first place, or reduce the impact if a network is infected. We have some advice for you.
Ransomware attacks are rampant throughout the healthcare industry, affecting a high percentage of organizations.
After a healthcare provider becomes a victim of ransomware, the response is typical – these organizations recognize that attacks could occur again, with impacts even more severe, and invest both in safeguards to prevent future attacks and protections to mitigate the impact should they occur.
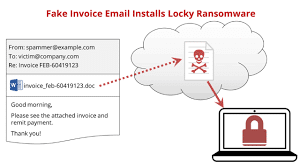
Research shows that a massive spam campaign with “locky ransomware” has been targeting healthcare organizations. We review malware and countermeasures.
Eagle’s opinion is that the agreement meets the minimum requirements of a HIPAA BAA, and as such Google accepts the minimum liability in the event of a data breach which is to send you “applicable Breach notifications” via email in the event of a breach. Google will not indemnify you, reimburse you for your breach notification costs, or pay any other damages.
The Office of Civil Rights issued a Fact Sheet regarding Ransomware and HIPAA. During 2016, ransomware attacks have increased 300% and healthcare organizations are being targeted. This increase in threat activity increases the consequences of a weak security... Read More