Details about the Heartbleed bug, a serious vulnerability in the popular OpenSSL cryptographic software library, were published earlier this week. This vulnerability has the potential to affect web users worldwide. The bug, caused by a programming error, allows the... Read More
Large hospitals and national organizations would benefit from a single, national security breach response process. The recent breaches at Target, Neiman Marcus and other retailers have gotten the attention of our national legislators. Last month, US Legislators... Read More
Walgreens’ new pharmacy model may be unintentionally violating customers’ patient privacy rights. Named the “Well Experience,” this new store layout/business model gets pharmacists out in the store, with the intention of increasing the pharmacists’... Read More
By eagleconsultingpartners | Published: April 4, 2014 Skagit County, located in Northwest Washington, has agreed to settle potential violations of the HIPAA Privacy, Security and Breach Notification Rules. The County was fined $215,000 and must work closely with the... Read More
By eagleconsultingpartners | Published: April 2, 2014 Undisclosed breaches are common in large healthcare enterprises according to recent survey According to a recent security survey by ThreatTrack, nearly 6 in 10 enterprise malware analysts from healthcare... Read More
In just under 3 weeks, Microsoft will end the Windows XP era ending support for both Windows XP and Microsoft Office 2003 on April 8, 2014. Most Microsoft products have a life cycle of about a decade, but these two products have been around longer. What prompted the... Read More

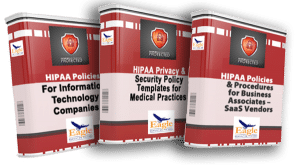 Eagle works with clients in healthcare and healthcare business associates to ensure HIPAA Security compliance. We provide a set of policy templates for a variety of business associate types including Cloud Vendors, Third Party Administrators, and Information Technology companies.