
HIPAA Policy Templates for IT Managed Service Providers
Written for IT companies that support healthcare clients: MSPs, IT consultants, value-added resellers, and software authors. Under HIPAA, you are a business associate, and you need written policies of your own.
Policies built around how IT providers actually work.
These policies are designed to meet the regulatory requirements of IT managed service providers who serve physician practices, hospitals, insurance plans, and other covered entities and business associates. That includes IT consultants, managed services companies, value-added resellers, and authors of medical or insurance software. (Cloud and SaaS vendors have their own set: see Healthcare Cloud Computing Vendors.)
They are completely different from policies designed for medical practices, hospitals, or insurance companies. Help desk protocols, secure configuration of client networks, RMM operation, cloud backup, data destruction, and handling of client credentials are all addressed directly.
What you get.
Quickly brings your organization into compliance with HIPAA rules for business associates.
Saves thousands of dollars in consulting fees.
Customize in Microsoft Word to fit the unique requirements of your business.
Satisfaction guaranteed by Eagle, a leading consultant for IT security policies in healthcare.
Business associates are audited and fined too.
OCR began its first random audits of HIPAA business associates in 2016. OCR can impose civil money penalties in four tiers based on culpability, from violations the organization did not know about to willful neglect that was never corrected. Amounts are adjusted for inflation each year, annual caps per violation type reach into the millions, and state attorneys general can bring their own actions. Written policies and procedures are one of the first things investigators ask to see.
What’s included.
Every policy is delivered in Microsoft Word, organized by audience so staff read only what applies to them.
Policies for all staff
- 1000Definitions for HIPAA Regulations and HIPAA Policies
- 1010Confidentiality and Security: General Rules
- 1020Minimum Necessary Policy
- 1030Confidentiality Safeguards (Oral and Written)
- 1050Computer Usage
- 1060Portable Computing Devices and Home Computer Use
- 1080Duty to Report Violations and Security Incidents
Policies for administrative management
- 1500Employee/Contractor Recruiting and Termination
- 1600Disclosures Required by Law
Policies for technical staff
- 2000Technical Support Procedures
- 2005Software Development Procedures
- 2010Secure Network Configuration for Client Networks
- 2020Cloud Backup Service
- 2025Managed Services Protocols
- 2030Remote Management and Monitoring (RMM) System Operation
- 2035Data Destruction Service
- 2040Authentication, Passwords and Encryption Keys
Executive management and Security Officer
- 2900Security Officer Appointment and HIPAA Documentation
- 3000Security Management Process
- 3005Data Backup
- 3010Disaster Recovery Plan and Emergency Mode Operation
- 3015Facility Security and Access Control
- 3020Periodic Security Evaluation
- 3025Audit Control and Activity Review
- 3030Malicious Software Protection
- 3035Breach Reporting
- 3040Security Awareness Program
- 3050Device and Media Disposal and Re-Use
- 3060Technical Safeguards
- 3070Business Associate Contracts
- 3075Employee System Access
- 3090Security Incident Response and Reporting
Appendices and forms
- Appendix A: Identifying Business Associates and Sample BAA
- Appendix B: Sample HIPAA Business Associate Agreement for Use with Customers
- Appendix C: Facility Security and Access Plan
- Appendix D: Workforce Access to PHI and Safeguards
- Appendix E: Miscellaneous
- Appendix F: Disaster Recovery Plan
- Disclosure Log
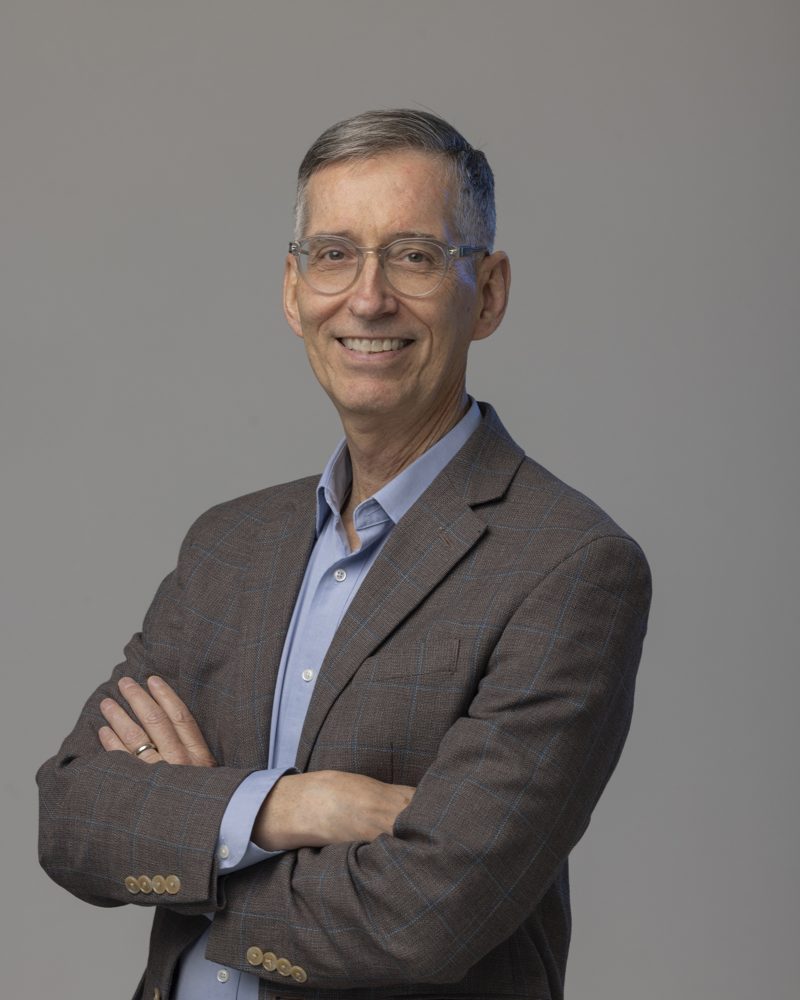
Gary Pritts, Founder and President
Gary Pritts is Founder and President of Eagle Consulting Partners. He began his HIPAA work providing technical input during the federal government's original drafting of the HIPAA regulations, and has since served more than 1,000 organizations as a consultant, as well as serving as a hospital trustee and as CSO for a cloud healthcare messaging company. Gary studied computer science at Purdue University and holds an MBA from Harvard Business School.
Gary partnered with dozens of VARs in the early 2000s when the HIPAA rules were first implemented, delivering HIPAA services to their physician practice customers. He also served as general manager of a VAR. These templates grew out of the policies he wrote for those VARs and for software-author and managed services partners.
HIPAA Policy Templates for IT Managed Service Providers
Instant download in Microsoft Word. Perpetual license for a single organization. Satisfaction guaranteed.
Save 20% ($100) with code Save-20 at checkout
Need policies built around your organization?
Eagle can tailor any template to your risk assessment, or write custom policies from the ground up. Call us, or send a note and we will follow up.
Talk to Eagle