Compliance
Regulatory compliance and audits: NYDFS Part 500, DOL guidance, HIPAA, Ohio requirements, SOC 2, and ISO 27001.
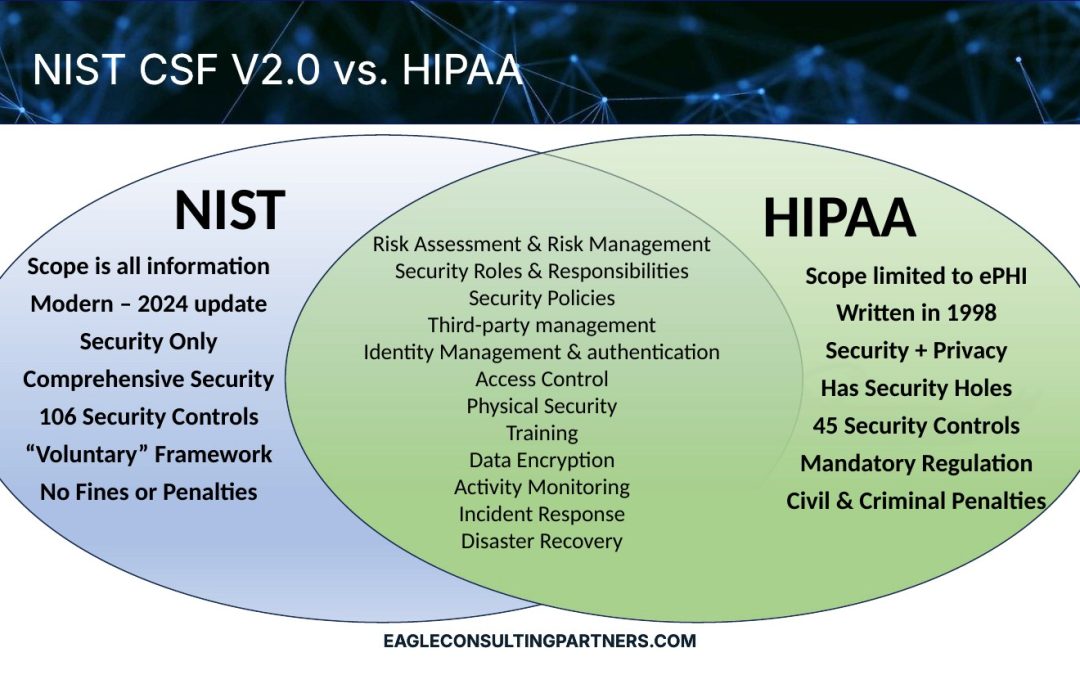
The HIPAA Security Rule Update: Where It Stands in 2026 and What to Do Now
HHS proposed the biggest overhaul of the HIPAA Security Rule in 20 years, but the final rule has slipped to 2027. Here is what was proposed and why you should not wait to prepare.
Read MoreNYDFS Part 500: The Final Requirements Are Now in Effect
As of November 1, 2025, the last phase of the amended NYDFS cybersecurity regulation is in force, including MFA for all users and a detailed asset inventory. Here is what covered entities need to have in place.
Read MoreOhio House Bill 96: New Cybersecurity Requirements for Ohio Local Governments
Ohio’s budget bill created ORC 9.64, requiring counties, cities, townships, school districts, and other political subdivisions to adopt a cybersecurity program, report incidents, and get formal approval before paying a ransom.
Read MoreOCR’s Risk Analysis Initiative: Why the HIPAA Risk Analysis Is Driving 2025 Enforcement
HHS OCR keeps settling HIPAA cases over the same failure: no accurate, thorough risk analysis. Here is what regulators are looking for and how to make sure yours holds up.
Read MoreDOL Cybersecurity Guidance Now Covers Health and Welfare Plans: What TPAs and Plan Sponsors Should Do
The Department of Labor confirmed its cybersecurity guidance applies to all ERISA plans, not just retirement plans. Here is what that means for plan sponsors, TPAs, and other service providers.
Read More