HIPAA
Redlined version of the HIPAA rules, as amended on 1/25/2013 by the HIPAA Omnibus Rule amendments. Eagle Omnibus Rule INDEX
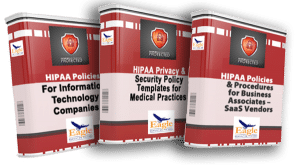 Eagle works with clients in healthcare and healthcare business associates to ensure HIPAA Security compliance. We provide a set of policy templates for a variety of business associate types including Cloud Vendors, Third Party Administrators, and Information Technology companies.
10 Cybersecurity Basics for Small Practices
Small medical practices are not immune from cyberattacks, but complex defensive recommendations can seem overwhelming. Here we break down our top 10 list of cybersecurity basics that will help small practices protect themselves from data breaches and other cybersecurity risks.
Read More
More Health Data Breaches Coming, 2018 Data Suggests
15 million health data records breached in 2018. “At least one breach per day.” We highlight the challenges so you don’t become a statistic!
Read More
New State of Ohio Standard Medical Release Form
The Ohio Department of Medicaid created two medical release forms. One form complies with the HIPAA requirements; the other form complies with 42 CFR Part 2 requirements regarding substance use confidentiality. These forms, if properly completed, must be accepted by any recipient in Ohio.
Read More
2018 Was a Record Year for HIPAA Penalties
OCR totaled a record $28.7 million in HIPAA enforcement actions in 2018. OCR targets a wide variety of organizations. Eagle Consulting Partners offers an array of services to assist you with HIPAA compliance.
Read More