Who are the Threats to Public Health Information?
A key component of any risk analysis and risk management program is understanding who the threats to your organization’s PHI data are.
Read More
Redlined version of the HIPAA rules, as amended on 1/25/2013 by the HIPAA Omnibus Rule amendments. Eagle Omnibus Rule INDEX
 Eagle works with clients in healthcare and healthcare business associates to ensure HIPAA Security compliance. We provide a set of policy templates for a variety of business associate types including Cloud Vendors, Third Party Administrators, and Information Technology companies.
A key component of any risk analysis and risk management program is understanding who the threats to your organization’s PHI data are.
Read More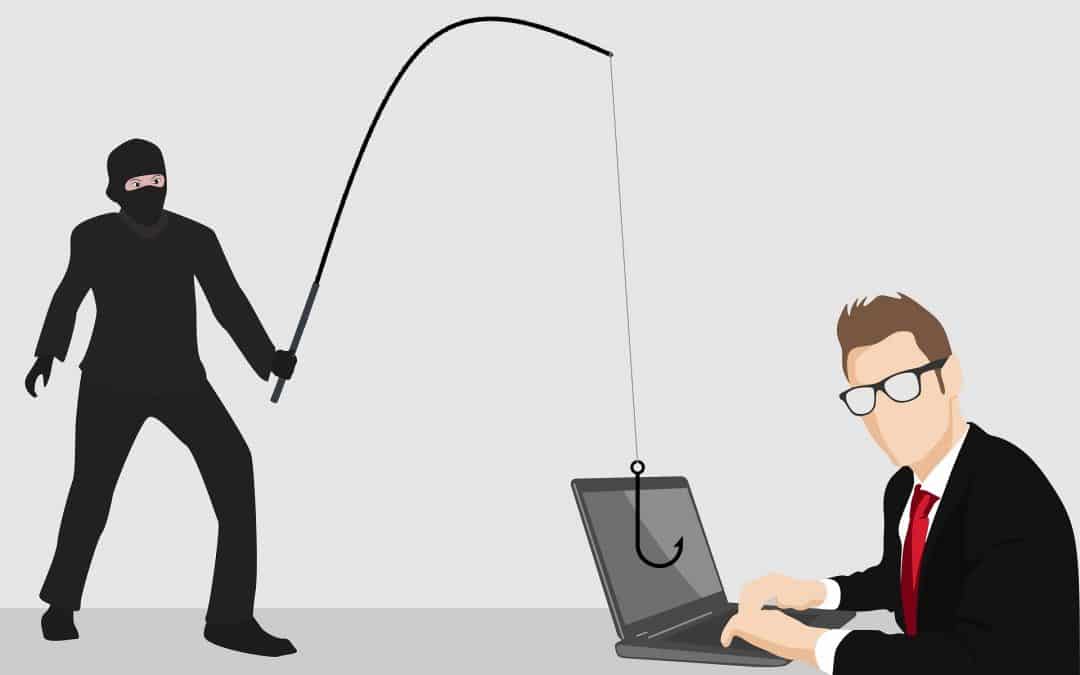
Phishing is a big threat to healthcare, and employees are the weak link. You need regular, effective security awareness training for staff. Eagle can help.
Read More
Email encryption is a major area of non-compliance for DD boards. Read more to explore some of the typical challenges and a possible solution.
Read More
Cyber-attacks on healthcare providers increased from 2016 to 2017, and are still trending upwards. Extensive private data plus inadequate security makes healthcare organizations attractive targets for attackers and, all too often, victims of their own errors.
Read More
HIPAA Business Associates have experienced HIPAA breach fines in the millions of dollars. Eagle Consulting offers HIPAA Policy Templates specifically tailored to different types of Business Associates, including cloud computing vendors, IT managed services companies, and third-party administrators.
Read More
Ohio DD Boards are responsible for ensuring confidentiality when working with third parties. The appropriate method varies depending on whether a 3rd party provider is HIPAA Covered Entity or not. Eagle offers a model confidentiality agreement for contract providers who are not HIPAA Covered Entities.
Read More