HIPAA
Redlined version of the HIPAA rules, as amended on 1/25/2013 by the HIPAA Omnibus Rule amendments. Eagle Omnibus Rule INDEX
 Eagle works with clients in healthcare and healthcare business associates to ensure HIPAA Security compliance. We provide a set of policy templates for a variety of business associate types including Cloud Vendors, Third Party Administrators, and Information Technology companies.
Security Risk Analysis: Doctors believe EHR outages harm patients
According to a recent survey, physicians believe that EHR downtime harms patients. This is supported by the the Office of the National Coordinator of Health Information Technology (ONC), which states that medication errors and other impacts can occur. An effective HIPAA Security Risk Analysis (SRA) will
Read More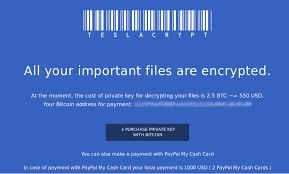
Ransomware – First Person Account
An Eagle Consulting Partners client, a 10 physician practice, shared their ransomware story. In the words of the system administrator: It was about 6PM on a Wednesday evening and I needed to do some maintenance on the EMR server. I was at home. Typically I wait... Read More
HHS issues Guidance regarding HIPAA and Cloud Computing
Healthcare organizations are increasingly using cloud computing vendors for electronic records, billing and revenue cycle management, file sharing, backup, and a wide variety of other functions — and HHS Office for Civil Rights (OCR) has released important new guidance for these companies.
Read More
Preventing and Mitigating Ransomware Attacks
Recently, entire hospital networks have been shut down for time periods between 3 days and 3 weeks due to ransomware attacks. What can be done? Fortunately, there are established best practices which can prevent one of these attacks in the first place, or reduce the impact if a network is infected. We have some advice for you.
Read More
HIPAA Compliance with Google’s G Suite (Google Apps)
Eagle’s opinion is that the agreement meets the minimum requirements of a HIPAA BAA, and as such Google accepts the minimum liability in the event of a data breach which is to send you “applicable Breach notifications” via email in the event of a breach. Google will not indemnify you, reimburse you for your breach notification costs, or pay any other damages.
Read More