HIPAA
Redlined version of the HIPAA rules, as amended on 1/25/2013 by the HIPAA Omnibus Rule amendments. Eagle Omnibus Rule INDEX
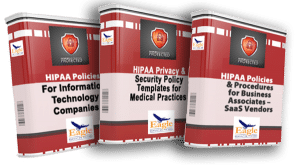 Eagle works with clients in healthcare and healthcare business associates to ensure HIPAA Security compliance. We provide a set of policy templates for a variety of business associate types including Cloud Vendors, Third Party Administrators, and Information Technology companies.
2016 is Biggest HIPAA Enforcement Year, $19 Million in Fines
While only in the 8th month of the year, 2016 is already the biggest HIPAA enforcement year as tallied by the dollar amount of fines, which exceed $19 Million. Here is a roundup of enforcement actions this year: Advocate Health Care, $5.55 Million. Advocate Health... Read More
OCR Details 5 Most Common HIPAA Mistakes
The Health and Human Services Office of Civil Rights (OCR) recently detailed the 5 most common mistakes that organizations make in their HIPAA compliance programs, as reported by TechTarget’s SearchHealthIT coverage. According to OCR, the 5 most common HIPAA... Read More
The HIPAA Internal Audit
Because the Honor System Doesn’t Work Electronic record systems contain a vast trove of interesting information – which can be a great temptation for a curious employee when they know that their relative, friend or neighbor was in the clinic. It has been 15... Read More
Vendor Risk Highlighted by Medhost Backdoor
This month Carnegie Mellon University’s CERT Division issued an advisory regarding a flaw in Medhost’s Perioperative Information Management System (PIMS). PIMS is a widely used suite of applications for surgery departments to manage surgical cases from... Read MoreHIPAA Breach Reports – Spring 2015
Despite the high stakes, some healthcare providers have been rather blasé about security. But, a failure to comply with HIPAA rules can lead not only to penalties of up to $50,000 per record depending on the level of negligence but also to a class action suit in a civil court and criminal charges. What can you do about that?
Read More