HIPAA
Redlined version of the HIPAA rules, as amended on 1/25/2013 by the HIPAA Omnibus Rule amendments. Eagle Omnibus Rule INDEX
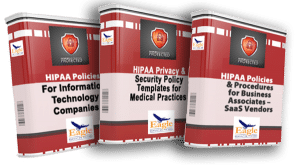 Eagle works with clients in healthcare and healthcare business associates to ensure HIPAA Security compliance. We provide a set of policy templates for a variety of business associate types including Cloud Vendors, Third Party Administrators, and Information Technology companies.
OCR Active with HIPAA Enforcement
Over the last 6 months the HHS Office of Civil Rights (OCR) has announced an average of a settlement or other enforcement action per month. While most affected organizations were hospital systems or national companies, one small organization also was included. Here is... Read MoreOrthopaedic Practice Fined $750,000 for HIPAA Violation
An Orthopaedic Practice fined $750,000 for HIPAA Violations, is learning the hard way that they needed to have a business associate agreement (BAA) in place. The settlement comes after an alleged breach 17,300 patient’s information.
Read MoreLincare Inc. Ordered to Pay $239k HIPAA Violation Fine
The cost of proactive measures are far less than what Lincare paid for a HIPAA Violation Fine. Lincare believed that it had not violated HIPAA because the PHI was “stolen” by an individual who discovered it on the premises — but they were wrong.
Read MoreCompliance Risk for Business Associates
Risk analysis for business associates is one of Eagle’s smart services, and it’s always needed both for business associate firms themselves and for the hospital, clinic and other healthcare entities relying on their associates for compliance to help avoid breaches and resulting government penalties. Compliance failures can cost up to $50,000 per incident.
Read MoreNew Eagle HIPAA Policy Templates
Eagle has added three new downloadable HIPAA Policy templates bringing the total to six now available, ranging from HIPAA Privacy & Security Policy Templates for Medical Practices to Confidentiality & Computer Security Policies for Ohio DD Boards.
Read More