
HIPAA and DOL Policy Templates for Third Party Administrators
Fully updated in December 2025. Written for small and mid-sized TPAs that administer health benefit plans covered by HIPAA and the Department of Labor’s cybersecurity guidance.
Procedures for the moments you act on behalf of the plan.
HIPAA regulates self-insured group health plans covering medical, dental, and vision, along with health savings accounts, flexible spending accounts, and other plan types. TPAs that administer any of these plans are business associates of the plan and must comply with HIPAA. The DOL regulates ERISA health plans, and both expect detailed, written policies and procedures.
These templates cover the requirements that apply to every business associate, plus procedures for the many situations where the TPA acts on behalf of the health plan, so those actions are handled in a compliant way.
Version 4.0 adds technology control updates for cloud security, ransomware prevention, safeguards for employees working from home, and current authentication technologies. It also reflects the 2024 changes regarding substance use disorder records. The reproductive health care privacy provisions, vacated in Purl v. U.S. Department of Health and Human Services, have been removed.
What you get.
Organized by audience to simplify staff training.
Quickly bring your technology into compliance with HIPAA rules for TPAs.
Saves thousands of dollars in consulting fees.
Customize in Microsoft Word to fit your business.
Satisfaction guaranteed by Eagle, a leading consultant on the HIPAA regulations.
Avoid HIPAA penalties.
Your organization is subject to both civil and criminal penalties for non-compliance. OCR can impose civil money penalties in four tiers based on culpability, from violations the organization did not know about to willful neglect that was never corrected. Amounts are adjusted for inflation each year, annual caps per violation type reach into the millions, and state attorneys general can bring their own actions. Written policies and procedures are one of the first things investigators ask to see.
Want training and a portal too?
The TPA Compliance Program bundles these policies with Eagle’s Security Risk Assessment Template, a year of the Eagle Training Portal, a HIPAA training video, and a test with training certification.
What’s included.
Every policy is delivered in Microsoft Word, organized by audience so staff read only what applies to them.
HIPAA policies for all staff
- 1000Confidentiality, Privacy and Computer Security Definitions
- 1010HIPAA: General Rules
- 1020Minimum Necessary Policy
- 1030Confidentiality Safeguards (Oral and Written)
- 1035Prohibitions on Use of Genetic Information and Sale of PHI
- 1040Speaking with the Family and Friends of a Participant
- 1050Authorizations
- 1060Verification
- 1065Employee Work at Home
- 1070Minors, Personal Representatives and Deceased Participants
- 1080Duty to Report Violations and Security Incidents
- 1090Disclosures that do Not Require an Authorization
Participant rights
- 1200Participant’s Right to Access Records
- 1210Participant’s Right to Request Amendment of Records
- 1220Participant’s Right to Receive an Accounting of Disclosures
- 1230Participant’s Right to Request Additional Restrictions
- 1240Participant’s Right to Request Confidential Communications
Confidentiality policies for supervisors
- 1300Mitigation
- 1340Privacy Complaints
Shared privacy and security policies
- 1350Policy Updating and Staff Training
- 1360Sanctions for Staff Violations of Privacy/Security Policies
- 1370Business Associate Agreements and Vendor Management
- 1380HIPAA Assignments and Documentation
Administrative management
- 1500Employee Background Checks
Security policies for the owner and Security Officer
- 2000HIPAA Security Officer and Security Management Process
- 2010Data Backup Policy
- 2020Disaster Recovery and Emergency Mode Operation Plans
- 2030Facility Security and Access Control
- 2040Periodic Security Evaluation and/or Third-Party Audits
- 2050Audit Control and Activity Review Policy
- 2060Malicious Software Protection Policy
- 2070Security Awareness Program
- 2080Device and Media Disposal and Re-Use
- 2085Encryption and Key Management
- 2087User Account Management
- 2088Privileged Account Management
- 2090Technical Safeguards
- 2092Technical Controls for Mobile Devices
- 2095Change Management
- 2100Breach Reporting
Executive management and Security Officer
- 3010Employee System Access and Termination Procedures
Security policies for all staff
- 3080Computer Usage
- 3082Use of Social Media
- 3085Computing Devices and Workstations: Company-owned and BYOD
- 3090Security Incident Response and Reporting
Appendices and forms
- Appendix A: Identifying Business Associates
- Appendix B: Sample HIPAA BAA for Use with Subcontractors
- Appendix B2: Sample HIPAA BAA for Use with Customers
- Appendix C: Sample Privacy and Security Officer Duties
- Appendix D: Facility Security and Safeguards for Oral and Written PHI
- Appendix E: Workforce Access to PHI and Safeguards
- Appendix F: Minimum Necessary: Procedures for Routine Disclosures and Requests
- Appendix G: Miscellaneous
- Authorization Form
- Disclosure Log
- Participant Privacy Instructions
- Confidentiality Agreement for Cleaning Agency
- Employee Acknowledgement of HIPAA Policies and Procedures
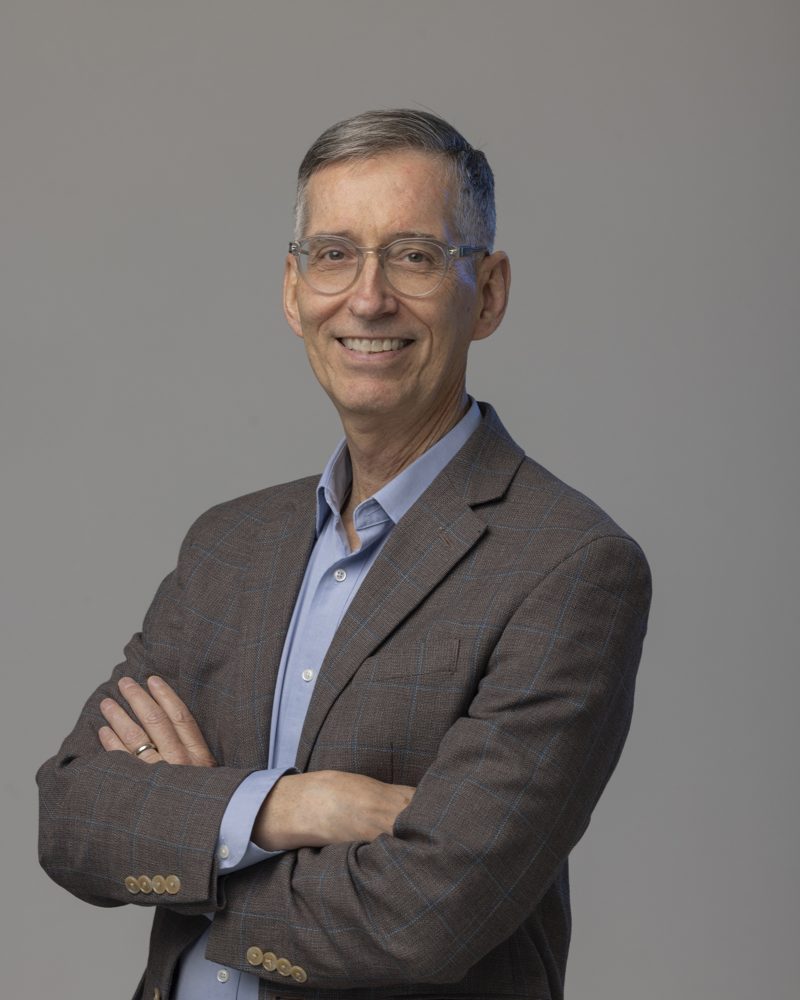
Gary Pritts, Founder and President
Gary Pritts is Founder and President of Eagle Consulting Partners. He began his HIPAA work providing technical input during the federal government's original drafting of the HIPAA regulations, and has since served more than 1,000 organizations as a consultant, as well as serving as a hospital trustee and as CSO for a cloud healthcare messaging company. Gary studied computer science at Purdue University and holds an MBA from Harvard Business School.
Gary understands TPAs from on-site consulting with multiple agencies. His knowledge of both the HIPAA rules and the ERISA regulations shaped these templates, with a special focus on IT security policies staff can carry out efficiently.
HIPAA and DOL Policy Templates for Third Party Administrators
Instant download in Microsoft Word. Perpetual license for a single organization. Satisfaction guaranteed.
Save 20% ($100) with code Save-20 at checkout
Need policies built around your organization?
Eagle can tailor any template to your risk assessment, or write custom policies from the ground up. Call us, or send a note and we will follow up.
Talk to Eagle